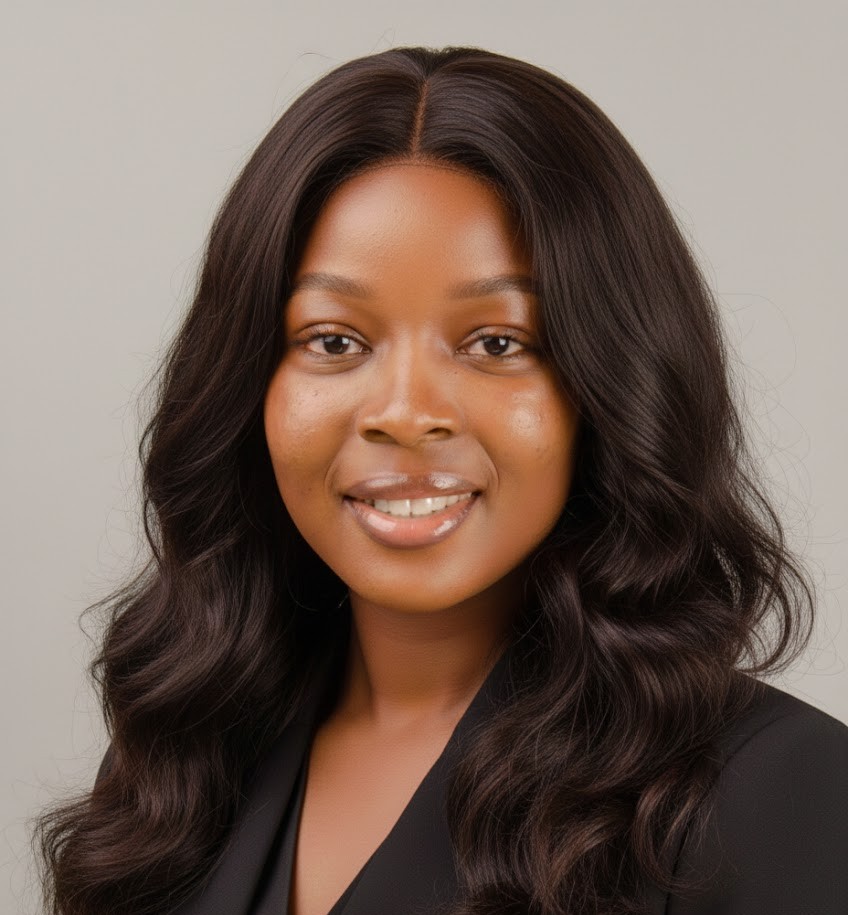
Jennifer Ugwoke

Cloud Security Analyst

AWS  |  IAM  |  Cloud Automation  |  Networking   |  Terraform

Designing and securing cloud environments with a focus on resilience, automation, least-privilege access, and practical security controls

Jennifer Ugwoke, Cloud Security Analyst

About

"Security is not a product, but a process and I am committed to making that process exceptional"

I am a resourceful cybersecurity professional with a hands-on approach to designing and implementing robust security solutions in AWS and Azure environments.

My expertise spans cloud architecture, threat detection, vulnerability management, and incident response.

Driven by intellectual curiosity and a deep commitment to protecting digital infrastructure, I approach every security challenge with precision, analytical rigour, and a continuous learning mindset.

Projects

Practical cloud and cybersecurity projects focused on building secure and resilient infrastructure.

Multi-Region Resilient Platform Architecture on AWS

TradeCore Africa's platform ran on a single EC2 instance with no regional redundancy, ahead of a Tier-1 bank partnership that required 99.95% uptime, a 15-minute recovery time and a 5-minute recovery point. This project took it from requirements to a documented, tested-by-design, bank-ready architecture.

What was done

  • Translated each business requirement into an architecture constraint and recorded eight architecture decisions, with their trade-offs.
  • Designed a multi-AZ primary region in af-south-1 on ECS Fargate and Aurora PostgreSQL, with a pilot-light disaster recovery region.
  • Secured the design with four customer-managed KMS keys, network isolation, least-privilege IAM, WAF, CloudTrail and Config.
  • Built the primary region as reusable Terraform modules covering networking, compute, database, cache, storage, security and monitoring.
  • Planned the validation: a 10× load test, AZ and database failure experiments, and a timed DR failover with an RPO check.
AWSCloud ArchitectureHigh AvailabilityDisaster Recovery

Cloud Infrastructure and FinOps Architecture

A secure, observable deployment for TradeCore Africa's 14-day pre-audit window ahead of an institutional banking review, held to a hard $25 AWS budget. The aim was to spend only where it creates application value and automate governance before provisioning.

What was done

  • Deployed a containerised Node.js API on ECS Fargate behind an ALB with ACM TLS, a React frontend on Amplify, Cognito for identity and a private RDS PostgreSQL database.
  • Removed the NAT Gateway cost (about $32.40 per AZ each month) by running ECS in public subnets, with security groups allowing only ALB-to-ECS and ECS-to-RDS traffic, recorded as an accepted decision.
  • Built a keyless GitHub Actions pipeline using OIDC, with staging, a manual approval gate and production promotion. A rollback drill restored traffic in 2m 34s.
  • Set budget alerts at 50% and 90%, five CloudWatch alarms routed through SNS to Slack, and scheduled staging to scale to zero overnight.
  • Wrote the teardown and post-funding plan. Adjusted net cost came to $8.32 a month.
AWSCloud InfrastructureFinOpsCloud Security

VaultCloud: Cloud Security Assessment, Remediation and Independent Validation

A deliberately misconfigured startup AWS environment (us-east-1, 18 primary resources, no prior security function), assessed, hardened and independently validated against realistic attack scenarios. A Prowler baseline scan returned 188 findings, including 23 Critical and 38 High, traced to four root causes: unrestricted network ingress, a publicly accessible unencrypted database, AdministratorAccess on both workload roles, and an AWS key exposed in Terraform source.

What was done

  • Cleared all Critical and High container vulnerabilities (232 Critical and 1,978 High CVEs down to zero) by rebuilding the API image as a distroless multi-stage build and removing 8 hardcoded secrets from the Dockerfile.
  • Added a Trivy scan to the CI/CD pipeline that blocks merges on unaccepted Critical or High CVEs, with 21 remaining OS-level CVEs formally risk-accepted with a reachability justification.
  • Replaced AdministratorAccess on the workload roles with a scoped least-privilege policy, then proved it with a trust-policy test and a permission-boundary test, where simulated destructive and escalation actions all returned implicitDeny.
  • Built an event-driven, self-healing S3 response: EventBridge detects Block Public Access being disabled and a Lambda restores it, with detection-to-remediation in 9 seconds across 5 of 5 successful invocations.
  • Redesigned the network to Zero Trust, restricting the app security group to port 5000 and the database security group to port 5432 from the app only, and confirmed it with CLI queries and Reachability Analyzer.
  • Independently red-team validated each fix, and tracked one finding openly: the original public database instance, still awaiting retirement.
AWSVulnerability ManagementIAMSecurity AutomationZero Trust

Skills

Cloud & Infrastructure

  • AWS
  • Microsoft Azure
  • Cloud Architecture
  • Cloud Infrastructure
  • Terraform

Cloud Security

  • Cloud Security
  • Identity & Access Management
  • Threat Detection
  • Vulnerability Management
  • Incident Response

Security & Compliance

  • Information Security
  • Security Controls
  • PCI DSS
  • ISO/IEC 27001
  • Risk Management

Security Automation

  • AWS Lambda
  • Amazon CloudWatch
  • Amazon EventBridge
  • Step Functions
  • Security Monitoring

Certifications & Training

Microsoft Azure Security Engineer

AZ-500

2024

Certified in Cybersecurity

ISC² CC

2024

AWS Certified Security Specialist

AWS Security Training

2024

Identity and Access Management

IAM Training

2024

Cybersecurity Soft Skills

Professional Training

2024

Let's Connect

Interested in cloud security, cybersecurity, collaboration, or discussing a project? I'd love to connect.